Email us at sales@ocgl.net
Email us at sales@ocgl.net
Blog
15Oct 2026
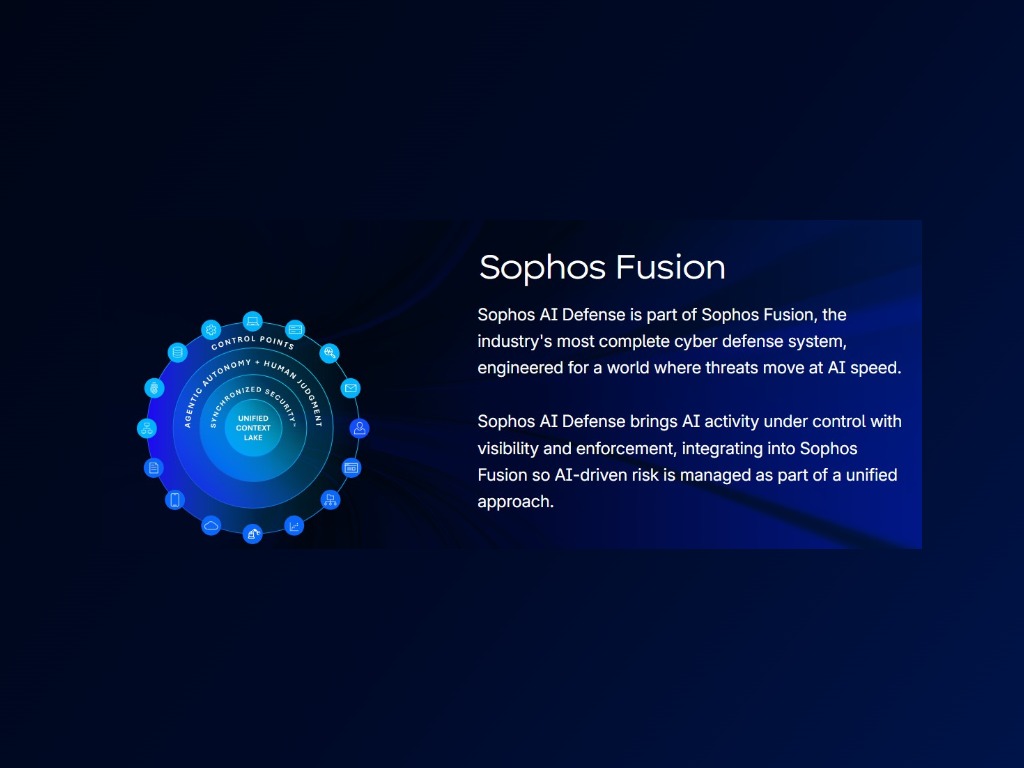
Shadow AI is any artificial intelligence tool, agent, or feature that staff use at work without approval from IT. It is now one of the fastest-growing risks for small and mid-sized businesses. On October 14, 2026, Sophos released Sophos AI Defense to help close that gap. In this article, we explain why unmanaged AI is a real concern, what can go wrong, and how Sophos AI Defense helps you find shadow AI and keep your team on the AI platform you trust.
Shadow AI works much like shadow IT. An employee signs up for a free chatbot, installs a browser extension, or turns on an AI feature inside a SaaS app. However, nobody in IT knows about it. As a result, nobody checks where the data goes, who can see it, or how long it is kept.
The difference today is scale. AI is now built into email clients, note-takers, design tools, and CRMs. Meanwhile, AI agents can act on their own. For example, they read files, send messages, and call other apps. So a single unapproved tool can touch far more data than a typical rogue app ever could.
Most staff are not trying to cause harm. In fact, they usually want to work faster. AI tools are free or cheap, easy to sign up for, and genuinely useful. However, adoption has moved much faster than policy.
The numbers show how wide the gap has become:
In other words, if you have not looked for shadow AI in your business, it is almost certainly there.
Unmanaged AI creates several kinds of risk at once. Here are the ones we see most often with clients.
Staff paste text into AI tools to get quick answers. That text may include customer records, source code, contracts, or financial data. Once it leaves your network, you may therefore lose control of it. In addition, some free tools keep prompts to train future models.
Canadian businesses must protect personal information under PIPEDA and provincial privacy laws. Furthermore, many firms follow SOC 2, ISO 27001, or industry rules. If client data flows into an unknown AI service, you may not be able to prove where it went. As a result, audits, contracts, and cyber insurance are all at risk.
AI agents often run with the same rights as the user who set them up. Consequently, an agent that can read a mailbox or a shared drive can also leak or change what it finds. Many of these agents run quietly in the background, so nobody reviews what they do.
Attackers use AI as well. This year, Sophos X-Ops tracked one attacker who used AI agents to build and test nearly 80 malware modules. Similarly, malicious browser extensions and fake AI apps are common lures. Every unknown AI tool is one more door you cannot see.
Finally, shadow AI fragments your investment. If you already pay for Microsoft 365 Copilot or another enterprise platform, staff using free tools on the side weakens your return. Moreover, company knowledge ends up scattered across services you do not manage.
Some firms respond by blocking every AI website. In practice, this rarely works. Staff switch to personal phones, new tools appear every week, and AI features keep arriving inside approved apps. On top of that, blanket bans cost you the real productivity gains that AI offers.
A better approach is to see what is in use, choose a preferred platform, and set clear guardrails around it. That is exactly the gap Sophos AI Defense is designed to fill.
Sophos AI Defense is an add-on for Sophos EDR, XDR, and MDR. It runs on Sophos Fusion, so it uses the protection you already have across endpoints, network, identity, and the browser. In other words, there is no separate platform to deploy. Sophos organizes the product around four steps.
First, AI Defense finds the AI tools, agents, and activity in your environment. This includes tools that IT never approved and agents that run on their own. For many businesses, this inventory alone is an eye-opener.
Next, it weighs context to decide what matters. It looks at who is acting, what permissions they hold, where they are, what data is involved, and how they behave. As a result, your team can focus on real risk instead of chasing every login to a chatbot.
Then, you set the rules. You can decide which AI tools are approved, and you can block or limit the ones that are not. Real-time guardrails inspect prompts, uploads, and other AI interactions to help stop sensitive data from leaking. This keeps staff on your preferred AI platform, such as Microsoft 365 Copilot, while protecting what they share with it.
Finally, AI activity feeds into Sophos XDR as a security signal. That way, it follows your existing detection and response workflows. For Sophos MDR customers, Sophos analysts can investigate and respond around the clock.
For more background on the platform underneath, read our guide to Sophos Fusion. You can also review our first look at what Sophos AI Defense does.
Technology works best alongside clear policy. We suggest five steps:
OPUS Consulting Group is a Vancouver-based Sophos Platinum Partner. We help businesses plan, deploy, and manage Sophos security, from endpoint and firewall to MDR. Our team can check whether your current Sophos licences qualify for AI Defense, help you choose a preferred AI platform, and build guardrails that suit how your people work. Learn more about our cybersecurity services and Sophos solutions, or see the official Sophos AI Defense product page.
Ready to see what AI is running in your business? Contact OPUS to book a shadow AI review.
Shadow IT is any unapproved software or device. Shadow AI is a subset focused on AI tools, agents, and features. It carries extra risk because AI tools often receive sensitive data in prompts and agents can act on their own.
Sophos AI Defense became generally available on October 14, 2026. It is an add-on for Sophos EDR, XDR, and MDR customers who have moved to the Fusion-enabled versions. Sophos is rolling out these upgrades in phases.
No. It lets you choose which AI tools are approved. You can then block or limit the rest and apply guardrails to prompts and uploads, so staff keep the benefits of AI without the risk.
No. It runs on Sophos Fusion and extends the endpoint, network, identity, and browser protection you already use. AI activity appears in Sophos XDR alongside your other alerts.
Most businesses do. Research from the Cloud Security Alliance found that 82% of organizations discovered AI agents or workflows they did not know about. A discovery scan is the fastest way to find out. OPUS can run one for you.

 1-866-800-OPUS (6787)
